Hide your
keys behind
a hash.
No need to scramble. An address that has never signed only reveals a hash of its public key. Once it signs, the key is public forever. If elliptic-curve signatures ever break, keys that are already public are the first targets. The fix is calm and preventative: check, migrate, keep it sealed.
Read-only. Always. Bunker Check never connects your wallet, never asks for a signature, never asks for a seed phrase. Anyone who does is not us.
Your migration officer.
Paste every address you own. The bot checks them all, scores your bunker, writes a migration plan for your wallet, and keeps watch. It runs in your browser: no account, no wallet connection, nothing stored on a server.
Before you sign.
Bunker Guard is a browser extension that warns before a sealed address signs anything. If a dApp asks your sealed address to sign, the guard intercepts the request and shows a blocking modal so you can cancel.
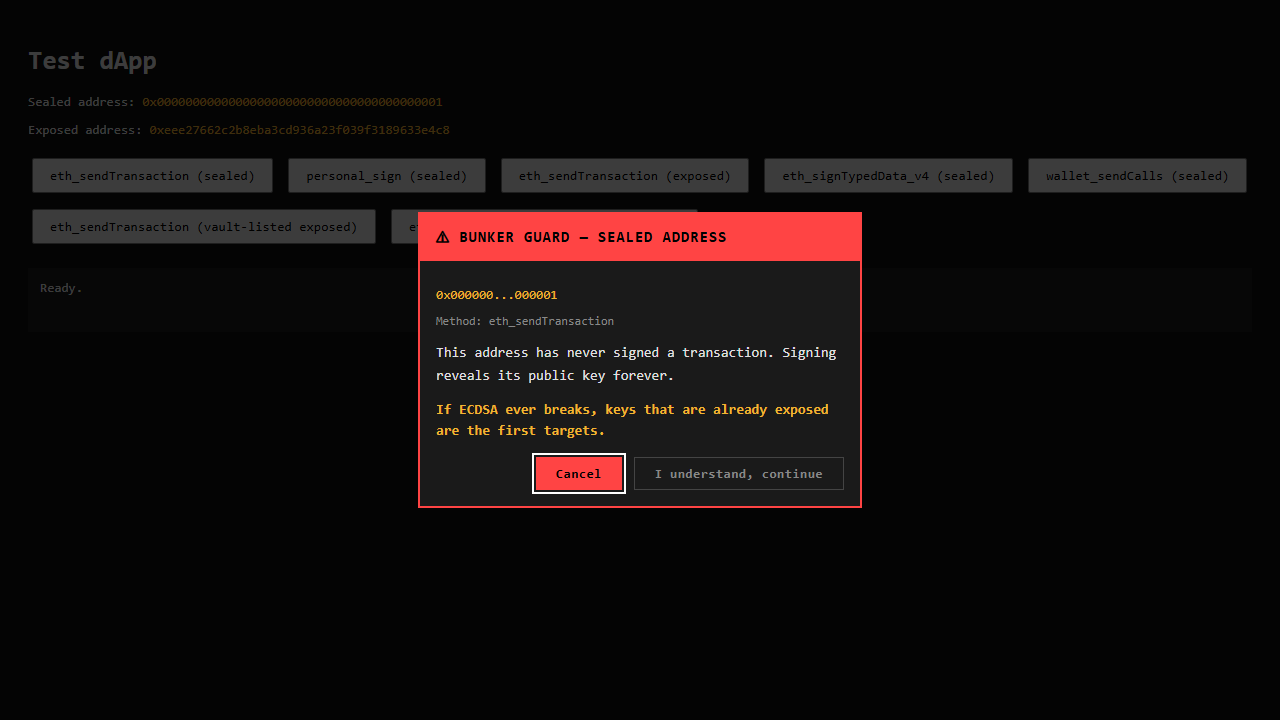
What it can't see
- WalletConnect / mobile signing — happens outside the browser.
- A malicious site can bypass the guard. It's a seatbelt for honest dApps, not a firewall.
Privacy
Only nonce and code lookups to public RPCs. No analytics, no telemetry, no remote code. Storage is local only.
Not on the Chrome Web Store yet — you install it manually.
Download ZIPBrave
- Open
brave://extensions - Enable Developer mode (top-right toggle)
- Click Load unpacked → pick the unzipped folder
Chrome
- Open
chrome://extensions - Enable Developer mode (top-right toggle)
- Click Load unpacked → pick the unzipped folder
Keys with no curve.
Hiding a key behind a hash buys time. The way out is signatures built only from hashes. The PQ Lab lets anyone verify a real hash-based signature on Ethereum — checked by a mainnet contract via read-only call. No wallet, no gas.
ECDSA vs lattice vs hash-based
SPHINCS+-style signatures rely only on the hash function (Keccak). There is no curve or lattice to attack. The trade-off is size. Structured math can hide shortcuts nobody has found yet; hashes are designed to have no structure. Where hash-based works, prefer it.
* ML-DSA-44 (FIPS 204) / Falcon-512. Sizes from the published standards. Hash-based column is measured live from the SPHINCS+C verifier on Ethereum mainnet.
Which addresses are already exposed?
The address format and its history decide whether your public key is already on-chain. Bunker Check reads this from public chain data.
| Address | Status | Why |
|---|---|---|
| ETH account, never sent a txnonce = 0 | SEALED | Only the hash of the key is known. Receiving funds doesn't reveal anything. |
| ETH account, has sent a txnonce > 0 | EXPOSED | Every signature lets anyone recover the public key. One outgoing transaction is enough. |
| EIP-7702 delegated EOAcode starts 0xef0100 | EXPOSED | Signing the delegation revealed the public key. |
| Smart wallet / Safecontract account | CHECK OWNERS | The contract holds no key, but its owner keys are exposed once they sign. Safety depends on the owners. |
| Other contractcontract account | CONTRACT | No key of its own. Safety depends on whoever controls it. |
| BTC P2PKH / P2WPKH, never spent1… / bc1q… | SEALED | The key stays behind a hash until the first spend. |
| BTC address that has spentor was reused after spending | EXPOSED | Spending reveals the public key. Coins still at that address are exposed. |
| BTC Taproot / P2PKbc1p… / early coins | EXPOSED | The public key is in the address itself, so it's exposed from day one. |
| Solana addressbase58 ed25519 public key | EXPOSED | A Solana address IS the public key. There is no hash in front of it — exposed from day one. |
| ETH on any EVM chainnonce > 0 on Base, Arbitrum, etc. | EXPOSED | The same key controls the same address on every EVM chain. If it signed on any chain, the key is public everywhere. |
Move in.
Don't rush.
Bunker rules
- Never type a seed phrase into a website.
- Never sign a "migration" for a stranger.
- Send a small test first.
- A rushed move is worse than no move.
- Multisig signers: rotate after each operation.
- Buy $BUNKER from a hot wallet, never from your vault: every swap is a signature and exposes that address.
Check every address you use
Hot wallets, cold storage, multisig owners. Write down which are exposed.
Derive a fresh address
In your own wallet, add the next account from the same seed. New wallets and new cryptography aren't needed.
Send a small test, then the bulk
Confirm the test arrived. Then move the rest, including tokens and NFTs, in one calm session.
Keep it sealed
Don't sign from the new address. Use it only to store funds.
Signed once? Rotate.
When you do sign, move whatever is left to the next fresh address in the same session.
Multisig signers: rotate after each operation.
Every Safe transaction exposes the signing keys. Replace exposed signers with fresh keys. Gather signatures off-chain and execute promptly. Type rotate <safe> in Bunker Bot to plan it.
The token
Own Uniswap v4 pool on Ethereum mainnet, run by the Bunker hook. Plain ERC-20, no owner, no mint, no pause, no proxy. Launch liquidity is Uniswap v4 position NFT #454274. It was burned (sent to 0x…dEaD) on 2026-10-12, so nobody can remove the liquidity, including the dev (burn tx). The status below is read live from the chain.
Fair launch: team holds 0 tokens at launch (unless a dev buy is announced). 1% of every trade in ETH goes to the treasury / Audit Fund. Exact-input swaps only. The tool stays free and read-only for everyone.
Treasury fees earmarked for independent audits of Bunker Box, Bunker Vault, and Bunker Guard. No promises of returns.
Fake token warning
Only the contract address shown on this page is ours. Other projects use similar names — always check the address. Scammers may create tokens with the same name on any chain. Buy from a hot wallet, never your vault: every swap is a signature and exposes that address.
How we're different
- Read-only — never connects your wallet
- Deep Scan finds gasless and off-chain signature exposure
- Pre-Sign Check + Bunker Guard stop exposure before it happens
- Migration Safety pre-flight checks the destination
- Safe Rotation Planner for multisig key hygiene
- Multi-chain scanner: 7 EVM chains + Solana + BTC
- Fees fund independent audits